Access routes that match the incident
Separate trusted-admin, no-admin, policy-lockout and hybrid branches, with official support preparation.
Regain control. Check what remains. Restore deliberately.
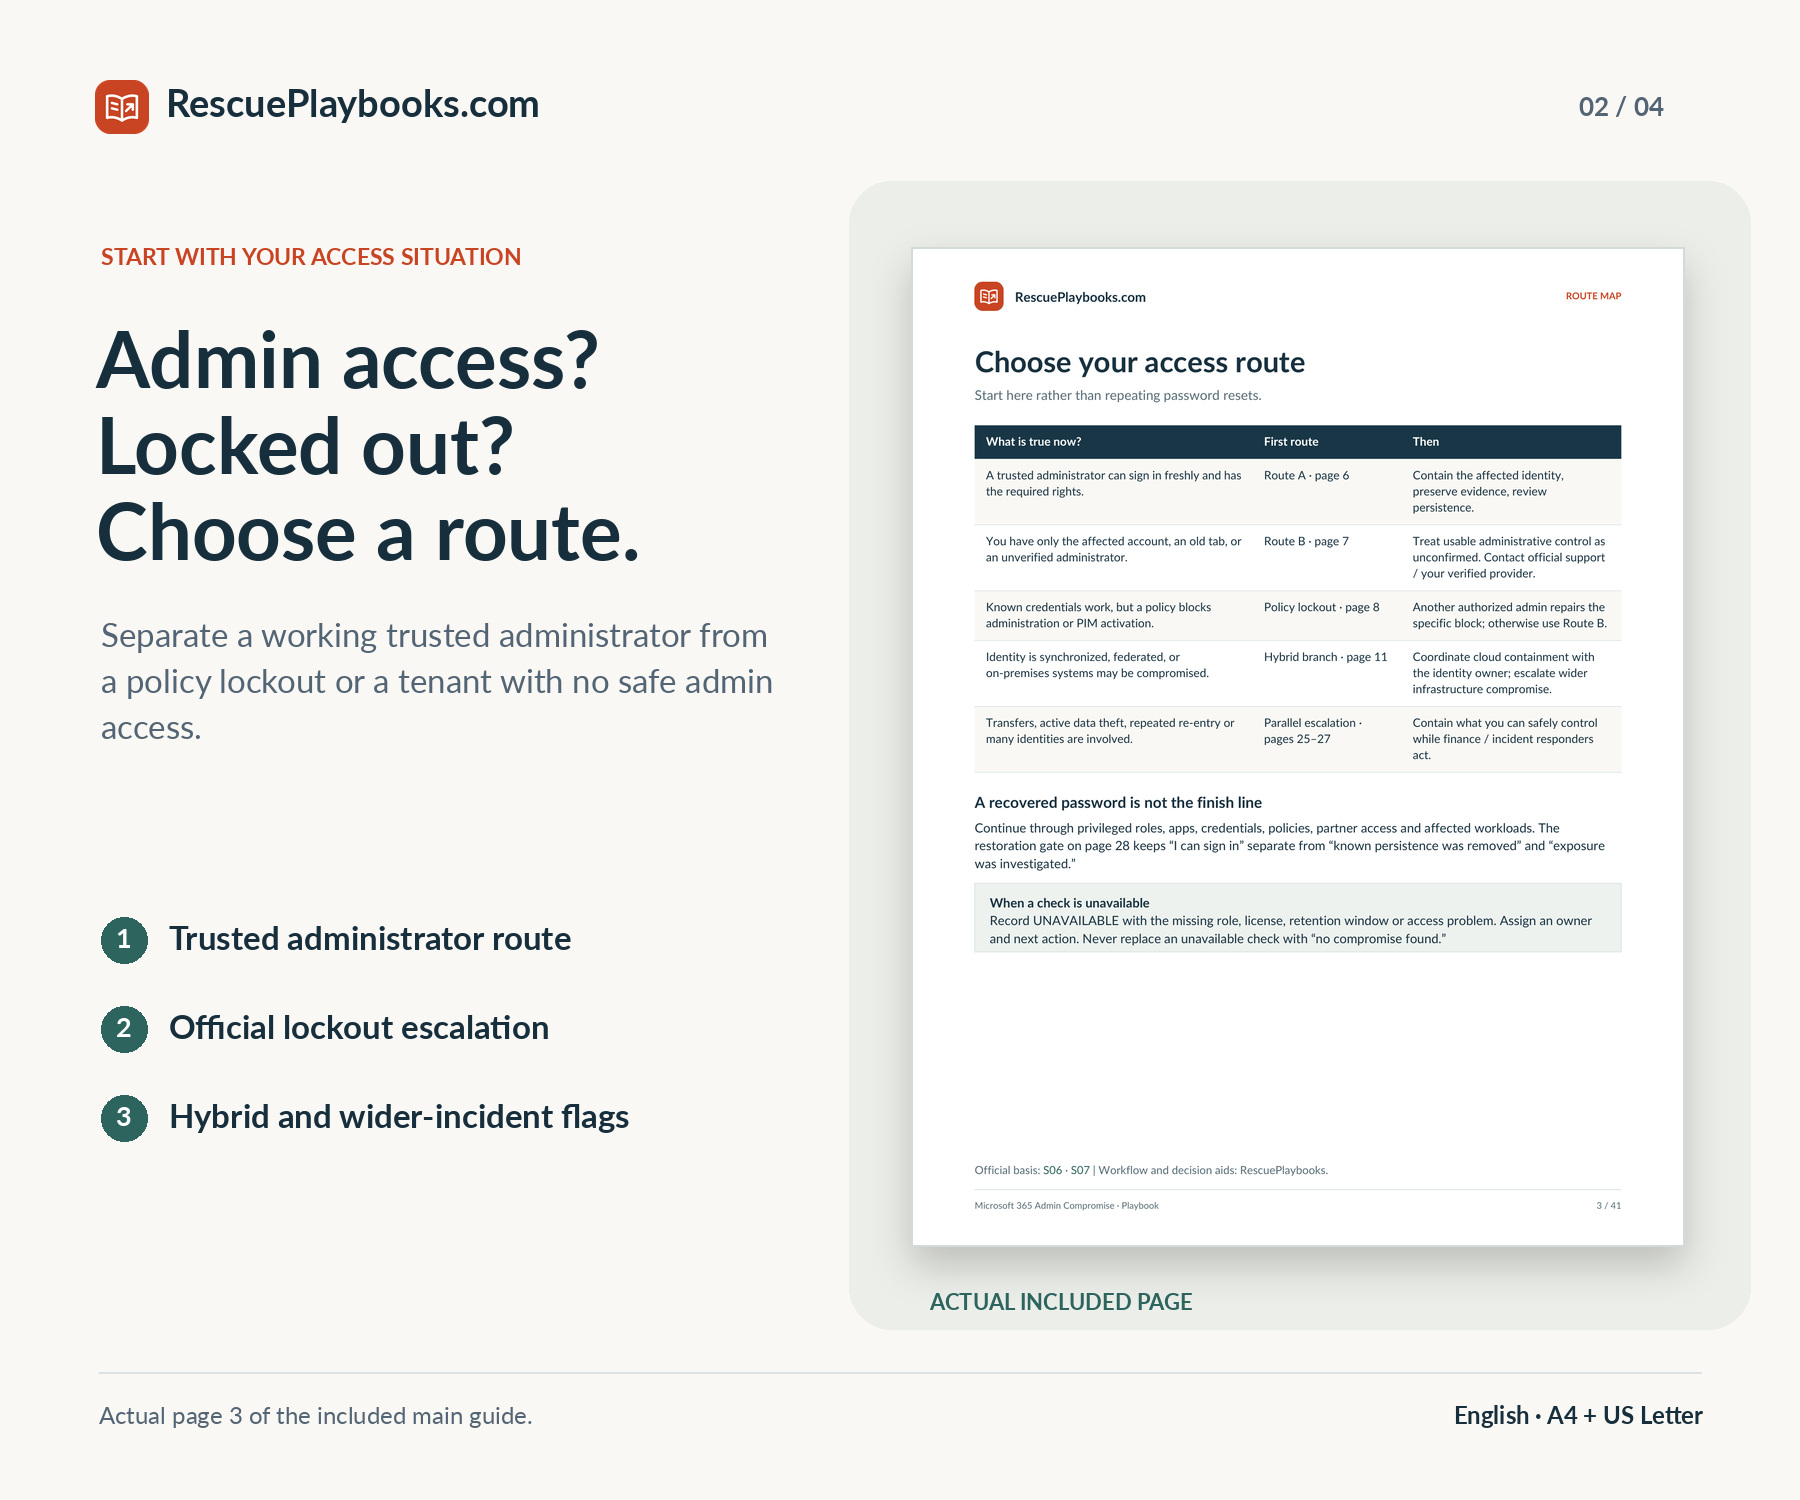
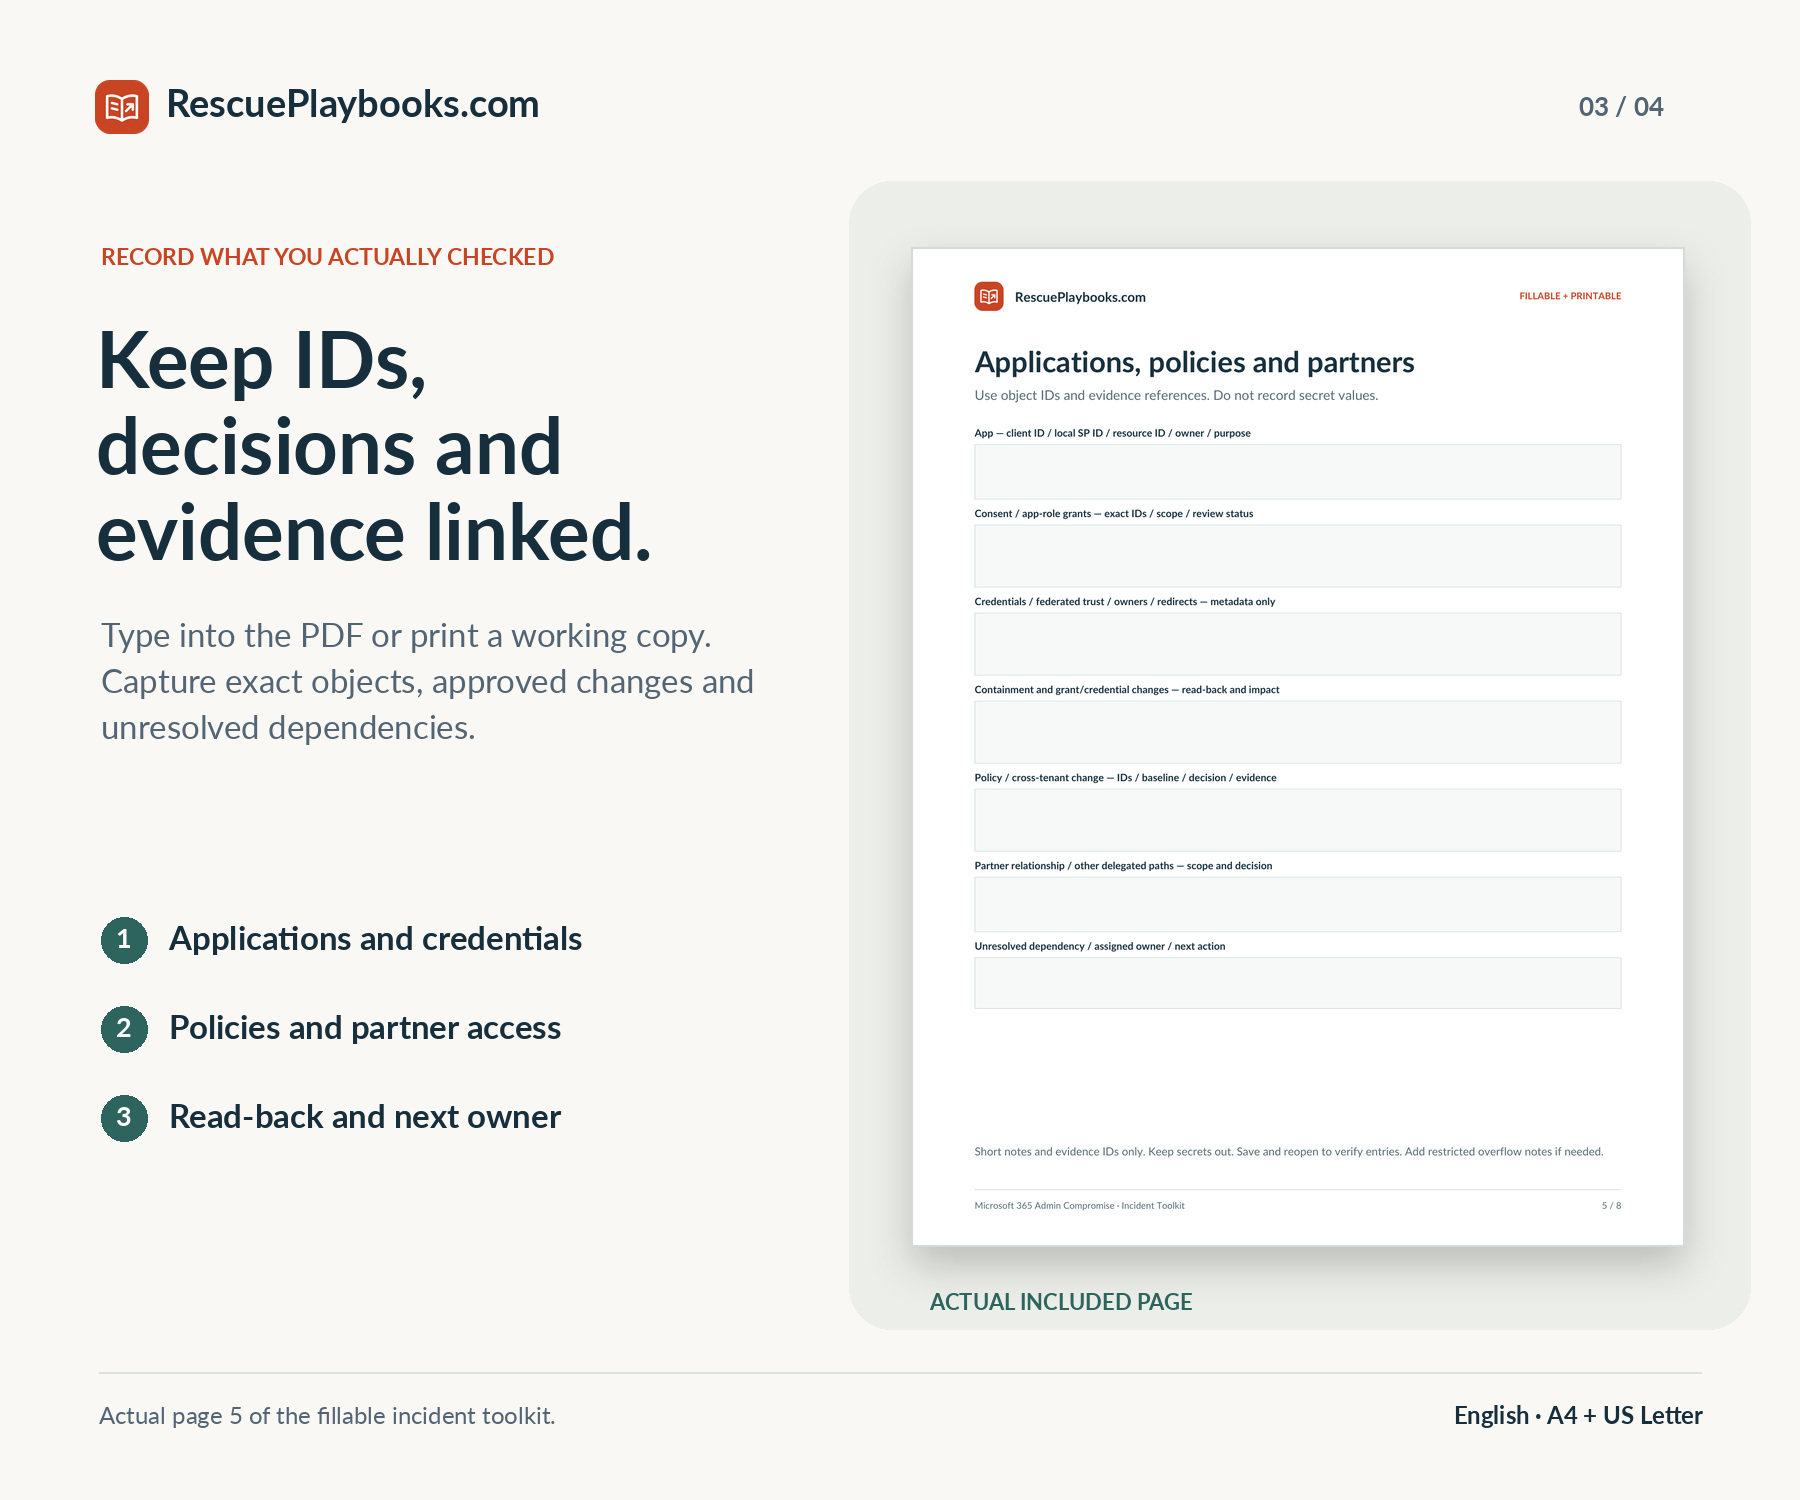
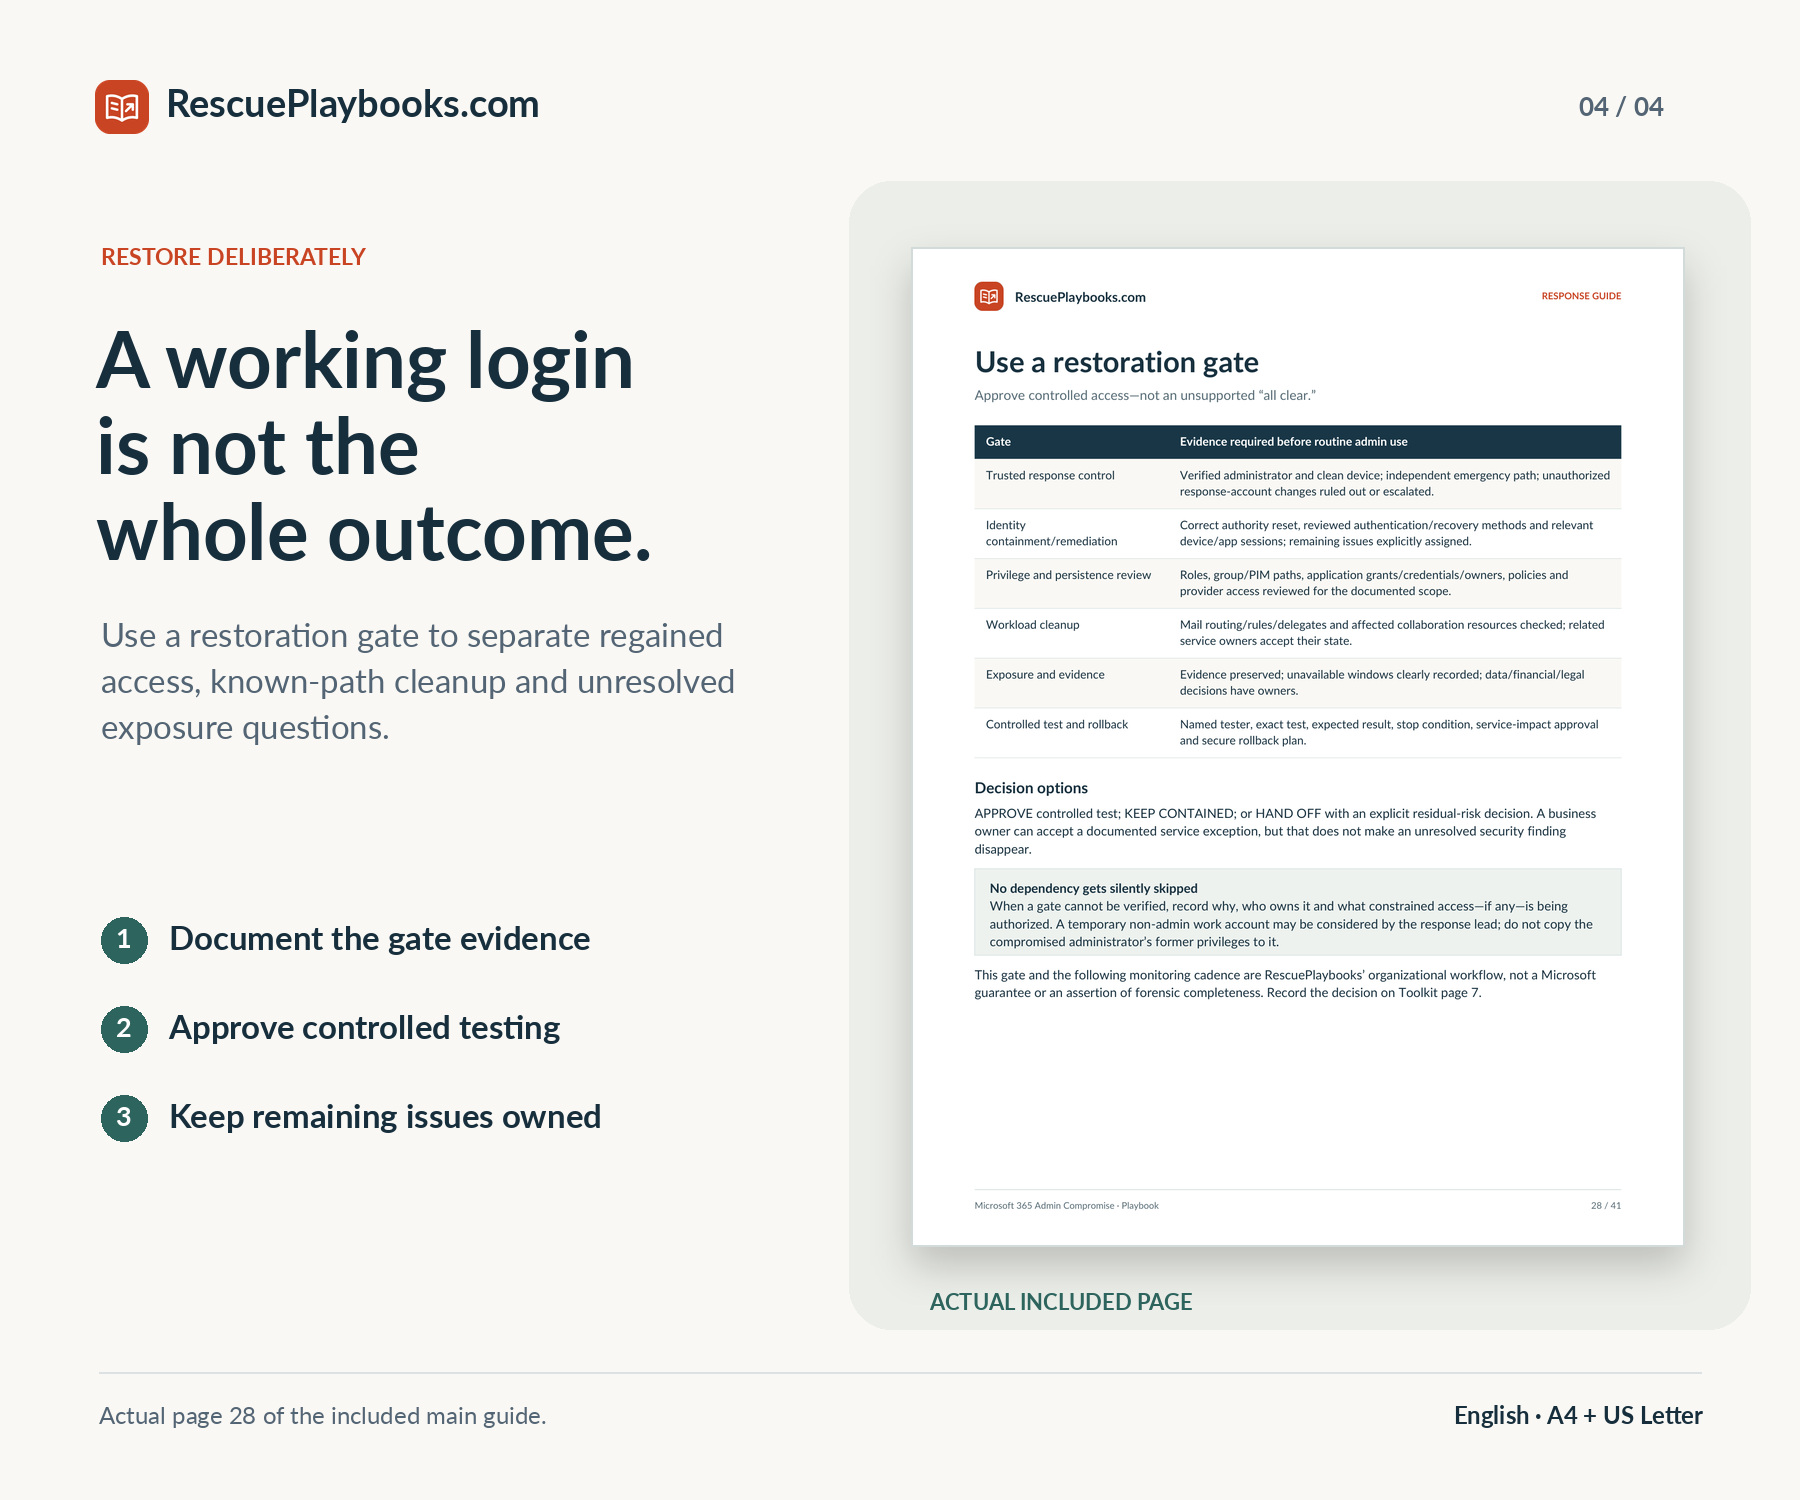
Choose the route for a working trusted administrator, a policy lockout or no safe admin access. Work through identity containment, privileged roles, applications, mail and sharing, then use evidence records and restoration gates to make the next decision.
Not an incident response or account recovery service. We do not access your tenant, change settings, contact Microsoft or act on your behalf.
Access recovery, removal of every attacker access path and data recovery are not guaranteed. Your privileges, identity architecture, available records and official verification affect the outcome.
Independent guide. Not affiliated with or endorsed by Microsoft. You are buying an independently organized PDF guide, writable incident records and adaptable messages—not software, a Microsoft service or an emergency response team.
Access routes. Persistence checks. Evidence and restoration tools.
Separate trusted-admin, no-admin, policy-lockout and hybrid branches, with official support preparation.
Work through account controls, method review and the limitations of session revocation.
Inspect roles and group/PIM paths, application grants, credentials, policies and provider access.
Review forwarding, hidden rules, delegates, tenant routing and affected file-sharing resources.
Document the evidence required for a limited restoration decision and keep exposure questions separate.
Type or print records for ownership, changes, evidence, persistence, service impact and handoff.
Use clearly fictional cases to see how findings, unknowns and decisions connect.
Follow 36 official sources and use focused messages for Microsoft, providers, internal notices and handoffs.
Choose your paper size and keep the incident records beside you.
Source-linked guidance, worked scenarios and clear stopping points.
The same material in two paper sizes, plus Start Here.
Quick Start, fillable toolkit, worked example, adaptable messages and Start Here.
A4 and US Letter editions contain the same content. No audio file is included.
Hands-on tenant access, incident response services, remote support, Microsoft case handling or work performed on your behalf. A full forensic investigation, legal breach assessment, infrastructure rebuild, recovery of all deleted data or government/sovereign-cloud instructions. Microsoft licenses, paid support entitlements, software, audio files, ownership-verification bypasses or guaranteed recovery or containment.
Independent guide for authorized administrators. Not affiliated with or endorsed by Microsoft. Microsoft licenses and support services are not included.
You are an authorized administrator investigating unexpected sign-ins, authentication changes or actions on an admin account.
You need a structured route to contain the affected identity and review what else may have changed.
You need to prepare official Microsoft or verified-provider escalation without using ownership bypasses.
You need to distinguish a policy lockout from a password problem and avoid locking out the defenders.
You need to organize reviews of permissions, credentials, rules, delegates, partners and affected resources.
You need usable records, handoff messages and restoration decisions while assigning specialist work where necessary.